
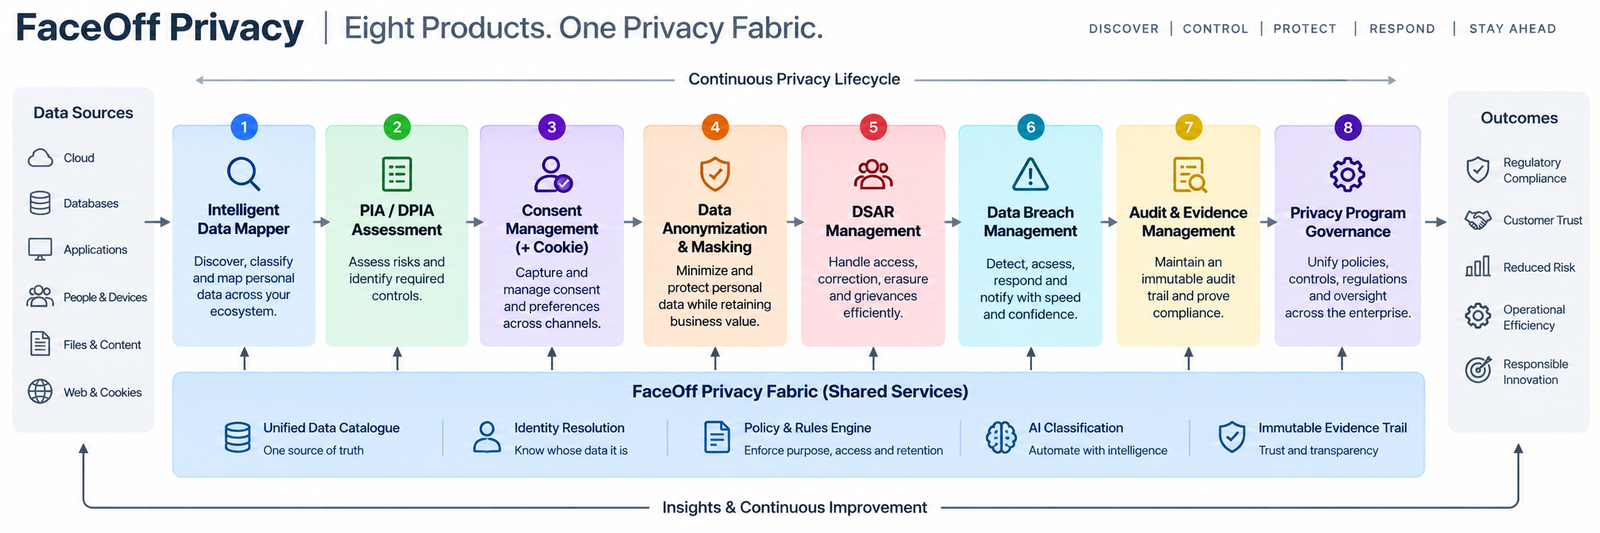
Enterprise privacy often fails not because organisations lack privacy tools, but because those tools operate in silos. Consent may sit in one system, personal data across dozens of applications, rights requests in another workflow and audit evidence somewhere else. FaceOff Privacy addresses this structural gap through a shared Privacy Fabric, connecting eight privacy products to a common operating layer.
Key Highlights
At its foundation is a shared data catalogue, identity resolution, policy engine, AI classification and immutable evidence trail. Instead of rebuilding information separately for consent, audits, breaches or Data Subject Access Requests (DSARs), the products operate against common records creating what FaceOff describes as one catalogue, one consent record, one policy engine and one audit trail.
The Intelligent Data Mapper provides the starting point by continuously discovering and classifying personal data across the enterprise. PIA/DPIA Assessment can then use that visibility to identify privacy risks and document mitigations before systems or processes are deployed.
Consent Management, supported by Cookie Management, captures purpose-specific permissions. When consent changes, the shared policy layer can connect that decision to the systems holding the individual's information. FaceOff illustrates this with consent withdrawal flowing through governance, data discovery and evidence management rather than becoming a manual ticket.
The next layer converts privacy policy into action. Data Anonymization & Masking protects sensitive information while retaining business utility, while DSAR Management coordinates access, correction, erasure and grievance requests using the same identity-resolved data map.
When incidents occur, Data Breach Management structures detection, assessment, notification and closure. Audit & Evidence Management simultaneously maintains the evidence trail required to demonstrate what happened, what controls operated and what actions were taken.
Finally, Privacy Program Governance provides the enterprise control plane connecting policies, controls and regulatory requirements. The result is a continuous cycle of Discover → Assess → Consent → Protect → Fulfil → Respond → Evidence → Govern, turning privacy from a collection of compliance tools into an interconnected operating architecture.